We may earn an affiliate commission when you visit our partners.
Course Discontinued We've found some alternatives for you:

Top Active Alternatives

Access Control and Identity Management is no longer accepting new enrollments. We've matched the highest-rated active courses in this subject:

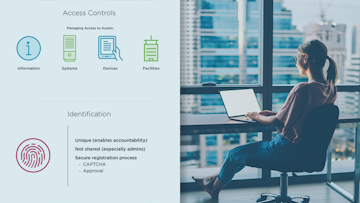
Course image
Kevin Henry

Traffic lights

Read about what's good
what should give you pause
and possible dealbreakers
Well-suited for learners who are interested in computer information security
Taught by instructors with experience in the industry
Examines risk and challenges of access control concepts
Develops methods for implementing and monitoring access control system
Explores different access control models and techniques
Requires learners to have working knowledge of access control

Save this course

Create your own learning path. Save this course to your list so you can find it easily later.
Save

Career center

Learners who complete Access Control and Identity Management will develop knowledge and skills that may be useful to these careers:
Identity and Access Management (IAM) Architect
An Identity and Access Management (IAM) Architect designs, implements, and maintains an organization's IAM system. This course will help build a foundation for someone in this role because it covers fundamental access control concepts, models, and techniques.
IAM Engineer
An IAM Engineer implements and manages an organization's IAM system. This course will help build a foundation for someone in this role because it covers fundamental access control concepts, models, and techniques.
Forensic Analyst
A Forensic Analyst investigates computer crimes. This course will help build a foundation for someone in this role because it covers fundamental access control concepts, models, and techniques.
Data Scientist
A Data Scientist analyzes data to identify trends and patterns. This course will help build a foundation for someone in this role because it covers fundamental access control concepts, models, and techniques.
Security Consultant
A Security Consultant provides advice and guidance to organizations on security matters. This course may be useful for someone in this role because it teaches the risks and challenges associated with access control concepts and the methods of implementing and monitoring an access control system.
Security Analyst
A Security Analyst is responsible for recognizing security risks, planning, and implementing security controls. This course may be useful for someone in this role since it teaches the risks and challenges associated with access control concepts and the methods of implementing and monitoring an access control system.
Risk Analyst
A Risk Analyst identifies and assesses risks to an organization's assets. This course may be useful for someone in this role because it teaches the risks and challenges associated with access control concepts and the methods of implementing and monitoring an access control system.
Chief Information Security Officer (CISO)
A Chief Information Security Officer (CISO) is responsible for the overall security of an organization's information systems. This course may be useful for someone in this role because it teaches the risks and challenges associated with access control concepts and the methods of implementing and monitoring an access control system.
Information Technology (IT) Auditor
An Information Technology (IT) Auditor evaluates the security of an organization's information systems. This course may be useful for someone in this role because it teaches the risks and challenges associated with access control concepts and the methods of implementing and monitoring an access control system.
Compliance Officer
A Compliance Officer ensures that an organization complies with all applicable laws and regulations. This course may be useful for someone in this role because it teaches the risks and challenges associated with access control concepts and the methods of implementing and monitoring an access control system.
Privacy Officer
A Privacy Officer oversees an organization's privacy program. This course may be useful for someone in this role because it teaches the risks and challenges associated with access control concepts and the methods of implementing and monitoring an access control system.
Penetration Tester
A Penetration Tester evaluates the security of an organization's computer networks and systems. This course may be useful for someone in this role because it teaches the risks and challenges associated with access control concepts and the methods of implementing and monitoring an access control system.
Information Security Analyst
An Information Security Analyst plans and carries out security measures to protect an organization's computer networks and systems. This course may be useful for someone in this role because it teaches the risks and challenges associated with access control concepts and the methods of implementing and monitoring an access control system.
Cybersecurity Architect
A Cybersecurity Architect designs, implements, and maintains an organization's cybersecurity infrastructure. This course may be useful for someone in this role because it teaches the risks and challenges associated with access control concepts and the methods of implementing and monitoring an access control system.
Security Engineer
A Security Engineer designs, implements, and maintains an organization's security systems. This course may be useful for someone in this role because it teaches the risks and challenges associated with access control concepts and the methods of implementing and monitoring an access control system.

Reading list

We've selected 50 books that we think will supplement your learning. Use these to develop background knowledge, enrich your coursework, and gain a deeper understanding of the topics covered in Access Control and Identity Management.
Richer and Sanso demystify the OAuth 2.0 authorization framework from first principles, walking through token lifecycles, client types, scopes, and threat models. By building working clients, protected resources, and authorization servers in code, engineers master delegated access control for modern web APIs.
Authored by the NIST researchers who standardized Role-Based Access Control, the foundational text formalizes RBAC0 through RBAC3, separation of duty constraints, and role hierarchies. Indispensable for architects designing enterprise permission models and understanding the formal roots of modern authorization.
Ross Anderson's landmark third edition situates access control within broader systems security, examining Bell-LaPadula, Biba, Clark-Wilson, capability systems, and real-world failure modes. Rich case studies from banking, healthcare, and cloud infrastructure show why authorization policies fail under operational pressure.
A definitive guide to financial risk management, this handbook provides in-depth analysis of methods for measuring and managing risk in financial institutions. It covers various types of financial risk and crucial reference for professionals and advanced students in finance.
This manual comprehensive resource covering a wide range of compliance and ethics topics. Often updated annually, it serves as a practical guide and reference tool for compliance professionals. It is particularly useful for understanding the various components of a compliance program and staying current with best practices. This go-to reference for practitioners.
Updated in 2024 for hybrid cloud environments, Rais, Morillo, Gilman, and Barth replace perimeter trust with continuous, identity-aware access enforcement. Detailed chapters on device authentication, mutual TLS, workload identity, and authorization engines equip practitioners to implement Zero Trust networks.
This influential book challenges conventional notions of risk and probability by focusing on the impact of rare and unpredictable events ("black swans"). It argues that these events have a disproportionate impact on the world and that we are often ill-equipped to deal with them. It's a provocative read that encourages a different way of thinking about risk and uncertainty.
Provides a comprehensive overview of computer security, covering both the technical and managerial aspects of the field. It valuable resource for anyone who wants to learn more about computer security.
Provides a comprehensive overview of security analysis and portfolio management, covering topics such as asset allocation, performance evaluation, and risk management.
This handbook provides a comprehensive overview of risk management, covering topics such as risk assessment, risk mitigation, and risk financing.
Written for developers and application architects, this book focuses on designing and using identity management to protect applications and data. It covers account provisioning, authentication, authorization, and common problems to avoid. The book delves into essential identity management protocols like OAuth 2.0, OpenID Connect, and SAML 2.0, making it highly relevant for those working with modern applications and cloud identity.
Provides a foundational understanding of risk management and insurance principles, making it ideal for those new to the topic or seeking a broad overview. It covers basic concepts, traditional insurance, and introductory enterprise risk management, serving as a valuable textbook for undergraduate programs and a solid starting point for professionals.
This handbook provides a comprehensive academic overview of compliance, covering a wide range of topics and perspectives from leading researchers. It is valuable for deepening understanding and exploring the theoretical underpinnings of compliance. is suitable for advanced undergraduate students, graduate students, and researchers seeking a broad scholarly perspective.
A practical guide specifically for understanding and implementing the GDPR. is crucial for anyone dealing with the data of EU residents, offering step-by-step guidance on achieving and maintaining compliance with one of the most significant data privacy regulations globally. It is particularly useful for professionals and organizations operating internationally.
Neil Madden bridges cryptography and practical authorization for service-oriented systems, comparing JWTs, macaroons, capability-based security, OAuth 2.0, and OpenID Connect. Concrete Java implementations demonstrate how to enforce fine-grained access policies without leaking tokens or over-privileging services.
Focused specifically on operational risk in the financial services industry, this book provides a detailed guide to managing this critical area. It covers frameworks, techniques, and best practices for identifying, assessing, and mitigating operational risks. It's essential for professionals working in risk management within banks and financial institutions.
Focused specifically on the ISO 27001 standard for information security management systems, this guide details the controls and processes for implementation and auditing. It is essential for organizations seeking ISO 27001 certification and provides in-depth knowledge for compliance professionals in information security. valuable reference for those involved in information security compliance.
Challenges traditional, rules-based approaches to compliance and advocates for a more integrated, ethics-driven model. It's valuable for deepening understanding by exploring the 'why' behind compliance failures and offering practical strategies for building a more effective compliance culture within organizations. It is relevant for both students and professionals seeking to improve compliance programs.
Aligned with international standards like ISO 31000 and the COSO ERM Framework, this book offers a comprehensive introduction to enterprise risk management. It covers identification, analysis, and treatment of various risks, including emerging trends. It's suitable for students and risk professionals seeking a thorough grounding in ERM principles and practices.
Definitive resource for understanding access control, a critical component of identity management. It defines access control components, provides a business framework for implementation, and discusses legal requirements. Focusing on Identity and Security Management, it examines risks, threats, and vulnerabilities in information systems and IT infrastructures. This makes it a strong foundational text for those new to the field and a useful reference for professionals.
This textbook provides a comprehensive treatment of financial risk management, covering market, credit, and operational risks within financial institutions. It's widely used in undergraduate and graduate finance programs and solid resource for understanding the principles and practices of financial risk management.
Published in 2025, Archer, Kahrer, and Trojanowski tackle fine-grained data authorization across microservices and API gateways using OAuth, JWTs, and claim-based policies. Ideal for cloud-native engineers building Zero Trust data planes where every request is authenticated and authorized at the edge and service mesh.
Offers guidance on the various aspects of information law, including data protection and privacy. Given the increasing importance of data privacy regulations like GDPR and CCPA, this book is highly relevant for understanding contemporary compliance challenges in this area. It valuable reference for legal practitioners and compliance professionals dealing with data.
Provides comprehensive coverage of Microsoft Azure Active Directory (now Entra ID) and its role in identity and access management in cloud environments. It offers a practical approach with hands-on examples for managing and protecting identities and data in Azure. Given the prevalence of Azure in cloud computing, this book is highly relevant for those focusing on cloud identity management.
Offers a critical look at common risk management practices and argues for more quantitative approaches. It challenges conventional wisdom and provides insights into improving risk assessment and decision-making. It's valuable for both students and professionals looking to refine their risk management methodologies.
Focused squarely on identity federation and authentication layers built atop OAuth 2.0, the Manning volume unpacks ID tokens, PKCE, session management, and single sign-on flows. Developers gain hands-on fluency in integrating OpenID Connect safely across single-page apps, mobile clients, and backend APIs.
Provides real-world examples and case studies of how organizations have implemented enterprise risk management. It offers practical insights into the challenges and successes of ERM implementation, making it valuable for those involved in establishing or improving an ERM program.
Provides an overview of major IT security standards and frameworks relevant to cybersecurity compliance, such as ISO 27001, NIST, and PCI-DSS. It helps solidify understanding of the technical controls necessary for a robust compliance program in the cybersecurity domain. This is an important reference for IT security practitioners and compliance professionals in technology-focused roles.
Provides a comprehensive international perspective on data privacy laws, covering various jurisdictions beyond just the GDPR. It is valuable for understanding the global landscape of data protection compliance and the challenges of navigating different legal frameworks. This key reference for professionals dealing with international data transfers and privacy compliance.
Delves into practical issues and presents case studies related to the execution of Enterprise Risk Management programs. It provides insights from senior risk management professionals and explores how organizations measure the impact of ERM. It is particularly useful for understanding real-world challenges and best practices in ERM implementation.
Delves into the complexities of financial regulation and compliance, particularly the challenges of navigating multiple regulatory bodies. Written by a former Inspector General of the SEC, it offers practical guidance for compliance professionals in the financial services industry. It valuable resource for understanding the specific compliance landscape of finance.
Explores the art and science of prediction in various fields, from weather forecasting to finance. It examines why some predictions succeed while many fail, emphasizing the importance of probability and understanding uncertainty. It offers valuable lessons for risk managers who rely on forecasting and data analysis.
This handbook provides a comprehensive guide to the interconnected areas of governance, risk management, and compliance (GRC). It covers frameworks, best practices, and practical guidance for implementing an integrated GRC program. It's a valuable reference for professionals responsible for GRC in their organizations.
This cookbook provides actionable solutions for identity management and authentication in both on-premises and cloud environments using Active Directory. It covers managing forests, domains, trusts, schemas, and partitions, and includes topics like Group Policy, federation, and integrating with Azure AD. is highly practical and useful for IT administrators and professionals working with Microsoft environments.
Fowler and Green-Ortiz translate Zero Trust principles into actionable enterprise architecture, emphasizing identity governance, least-privilege segmentation, and policy decision points. Security architects learn how to align continuous verification with existing IAM directories and compliance workflows.
Provides a comprehensive overview of key concepts and techniques in financial risk management, covering market risk, credit risk, and operational risk. It offers practical insights into identifying, assessing, and mitigating these risks and valuable resource for students and professionals in finance.
Offers a broad introduction to the interconnected fields of governance, risk management, and compliance (GRC). It provides a high-level overview suitable for gaining a foundational understanding of how these elements are critical for organizational success and avoiding major pitfalls. It is particularly useful for students and professionals new to the comprehensive scope of compliance.
Considered a classic, this book provides a historical perspective on the development of risk management and probability. It traces the evolution of our understanding of risk from ancient times to the modern era, offering valuable context for the field today. It's an engaging read for anyone interested in the intellectual history of risk.
Offers a practical, step-by-step guide to planning, designing, and deploying IAM solutions. It breaks down complex concepts into manageable components, making systemwide implementation seamless. The hands-on approach and focus on real-world implementations make it a valuable resource for both beginners and professionals looking to understand the practical aspects of IAM.
Focused specifically on risk management within the context of projects, this book provides practical guidance and techniques for identifying, analyzing, and responding to project risks. It's a valuable resource for project managers and teams, often used as a reference or textbook in project management programs.
Explores the application of behavioral science to ethics and compliance programs. It offers a contemporary perspective on designing compliance initiatives that are more effective by considering how people actually make decisions. This must-read for compliance professionals looking to enhance the impact of their programs.
Google security and reliability engineers share battle-tested patterns for least privilege, multi-party authorization, and auditable access controls in large-scale production systems. Valuable for understanding how operational resilience and strict permission boundaries reinforce one another.
Ferraiolo, Hu, and Kuhn provide an authoritative treatment of Attribute-Based Access Control, detailing policy languages like XACML, subject-object-environment attributes, and dynamic policy evaluation. Essential reading for moving beyond static roles to context-aware enterprise authorization.
Explores how organizations can integrate risk management into their strategic planning process to gain a competitive advantage. It goes beyond traditional compliance-based risk management to focus on how managing risk can create value. It's relevant for senior management and strategists.
Released in 2025, Adjuder distills core Identity and Access Management concepts—provisioning, RBAC, federation, PAM, and lifecycle governance—into an accessible practitioner primer. Well suited for newcomers and IT generalists building foundational literacy in enterprise access governance.
Offers a deep dive into the intricate world of digital identity protection across various domains, including social networks, cloud computing, and the Internet of Things (IoT). Authored by experts from computer science, law, economics, and sociology, it provides a sharp analysis of advanced technical and legal measures, focusing on authentication techniques, identity federation tools, and privacy protection solutions. It addresses limitations of existing methods and highlights pressing research concerns, making it relevant for contemporary discussions.
A practical guide focusing on Know Your Customer (KYC) compliance, a critical component of AML and financial crime prevention. provides hands-on guidance for compliance professionals involved in customer due diligence and identity verification. It useful reference for those working in financial institutions and other regulated entities.

Share

Help others find this course page by sharing it with your friends and followers:

Similar courses

Here are nine courses similar to Access Control and Identity Management.
Cybersecurity and Its Ten Domains
Most relevant
Security Fundamentals and Identity Management
Most relevant
Practical Cybersecurity Fundamentals: Unit 1
Most relevant
Scrum Master Certification: Scrum Methodologies
Most relevant
Patient Safety and Quality Improvement: Developing a...
Most relevant
Wharton Business and Financial Modeling Capstone
Most relevant
Risk Management: Use of Access Controls to Protect Assets
Most relevant
PMP 35 Hours Master Course: PMP Certification Exam Prep
Most relevant
DeFi Investor 2025: Earn No Matter The Market Conditions
Most relevant

Pluralsight Buyer Protection & Guarantee

Verified partner policies & purchase protections

Enterprise Technology Platform
Free Trial & Audit

10-Day Free Trial

10-day free trial (up to 200 minutes of content) with access to the Skills video library and skill assessments. Cancel before day 10 to avoid automatic conversion.

Return & Refund Policy

Cancel Anytime (Non-Refundable Once Billed)

Cancel easily online anytime before the 10-day trial expires to prevent billing. Once subscription fees are paid, individual subscriptions are non-refundable (cancellation stops future renewals).

Buyer Protections

Verified Academic & Industry Partner

Skill IQ and Role IQ diagnostic benchmark assessments, hands-on lab environments, and curated learning paths designed by technology leaders.

Key Purchase Protections
10-day free trial on individual Skills plans
Skill IQ assessments to benchmark proficiency
Cancel anytime online before trial ends without fees
Hands-on interactive labs and enterprise-grade tech content
OpenCourser Verified Partner Policy details last reviewed: 2026-10-22
Our mission

OpenCourser helps millions of learners each year. People visit us to learn workspace skills, ace their exams, and nurture their curiosity.

Our extensive catalog contains over 50,000 courses and twice as many books. Browse by search, by topic, or even by career interests. We'll match you to the right resources quickly.

Find this site helpful? Tell a friend about us.

Affiliate disclosure

We're supported by our community of learners. When you purchase or subscribe to courses and programs or purchase books, we may earn a commission from our partners.

Your purchases help us maintain our catalog and keep our servers humming without ads.

Thank you for supporting OpenCourser.

© 2016 - 2025 OpenCourser